Sanctions Screening vs Transaction Monitoring
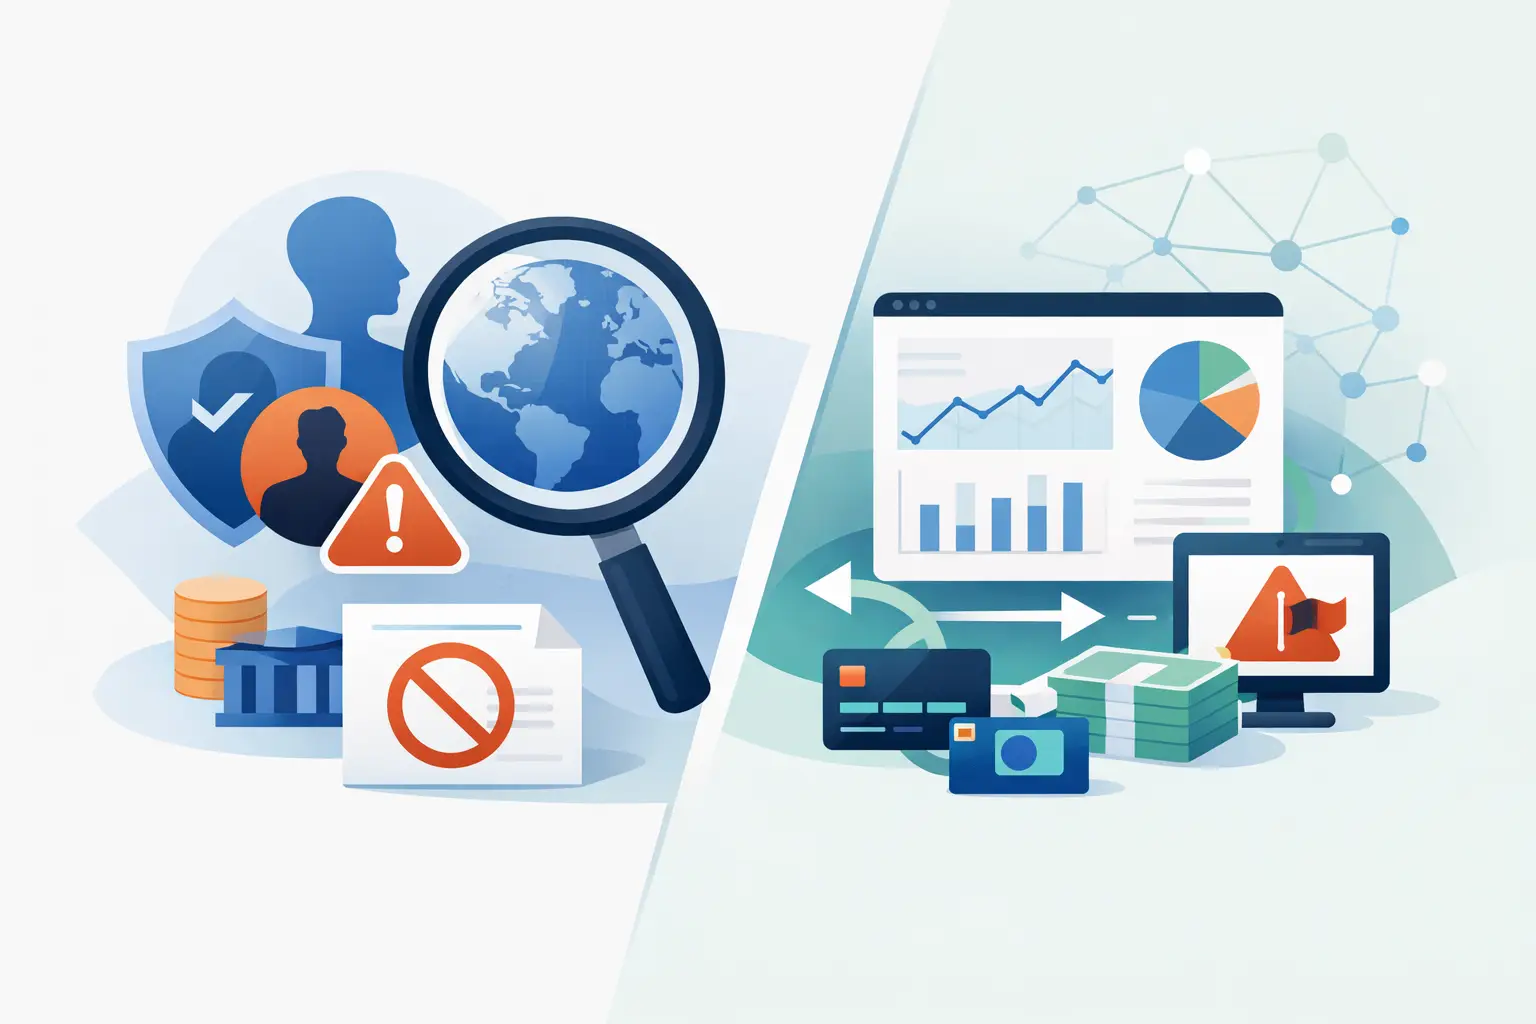
A payment can be cleared by a sanctions filter and still reveal money laundering risk. A customer can generate no unusual activity alerts and still be a prohibited party. That is the operational reality behind sanctions screening vs transaction monitoring: related financial crime controls with different objectives, data inputs, alert logic, and regulatory consequences.
Treating them as interchangeable creates blind spots. Treating them as separate systems with no shared intelligence creates duplication, inconsistent decisions, and weak audit evidence. Compliance leaders need a clear control model that distinguishes the two while connecting them where risk demands it.
Sanctions Screening vs Transaction Monitoring: The Core Difference
Sanctions screening asks a direct question: does a customer, counterparty, payment participant, vessel, entity, or other relevant party match a sanctioned person or restricted party? The control is designed to prevent prohibited dealings and, where required, identify property or interests that must be blocked, rejected, or reported.
Transaction monitoring asks a different question: does this activity appear unusual, inconsistent with the customer profile, or indicative of financial crime? It identifies patterns associated with money laundering, terrorist financing, fraud, sanctions evasion, structuring, mule activity, and other suspicious conduct. An alert is not a finding of wrongdoing. It is a prompt to investigate whether a potentially suspicious pattern has an innocent explanation.
The distinction matters because the response threshold is different. A confirmed sanctions match can require immediate action, often before funds move. A transaction monitoring alert typically requires investigation, documentation, and a decision on whether to file a suspicious activity report or take account-level action. Neither control can substitute for the other.
What Sanctions Screening Is Designed to Detect
Sanctions screening compares names and identifiers against applicable restricted-party sources. Depending on the institution’s business model, screening populations may include customers, beneficial owners, directors, counterparties, payment originators and beneficiaries, correspondent banks, trade parties, vessels, aircraft, and cryptocurrency wallet addresses.
Screening occurs at several points in the relationship. Customer and beneficial ownership screening is generally performed during onboarding and periodically afterward. Payment screening is performed before processing or releasing a transaction. Event-driven rescreening may be necessary when ownership changes, a new sanctions designation is issued, a customer expands into a higher-risk jurisdiction, or material data changes.
A strong sanctions screening program is not simply a list-matching exercise. It must account for transliteration, aliases, date of birth, nationality, geographic location, ownership and control, and the particular legal regimes that apply to the institution. A US financial institution may have obligations under OFAC rules, while a cross-border group may also need to consider UK, EU, UN, and local sanctions measures. The applicable scope depends on legal entity, location, currency, nexus, product, and transaction path.
False positives are expected. Common names, incomplete payment messages, and inconsistent formatting will produce alerts. The issue is not whether alerts exist, but whether the institution can resolve them accurately, quickly, and with a defensible record. A filter that produces too many alerts can delay legitimate payments and overwhelm investigators. A filter calibrated too aggressively to reduce volume may miss a true match.
What Transaction Monitoring Is Designed to Detect
Transaction monitoring evaluates behavior over time. Its scenarios may identify rapid movement of funds, unusual cash activity, round-dollar transfers, activity involving high-risk jurisdictions, transactions inconsistent with expected customer behavior, layered payments, or sudden changes in counterparty patterns.
Unlike sanctions screening, transaction monitoring rarely operates as a single-point comparison against a defined list. It uses rules, thresholds, risk scores, customer data, historical behavior, and increasingly analytical models. The quality of the outcome depends heavily on data completeness and customer segmentation. A $100,000 international wire may be ordinary for a multinational corporate customer and highly unusual for a newly opened retail account.
This is why scenario design and tuning cannot be static. Thresholds that work for one product, legal entity, or customer segment may be ineffective elsewhere. Compliance teams should validate that scenarios are aligned with the institution’s current risk assessment, products, delivery channels, customer base, and geographic exposure. They also need to investigate whether apparently low-risk activity forms a suspicious pattern when viewed across accounts or entities.
Transaction monitoring can surface sanctions evasion indicators, such as payments routed through unfamiliar intermediaries, sudden trade exposure to high-risk regions, or repeated transactions just below review thresholds. But an evasion indicator is not a confirmed sanctions hit. It should trigger enhanced review, which may include targeted sanctions screening and review of underlying parties, goods, ownership, and payment narratives.
Different Triggers, Different Decisions
The most practical way to separate the controls is to look at their triggers and outputs.
Sanctions screening is generally triggered by an onboarding event, a list update, a customer data change, or a proposed payment. Its output is a potential match that must be dispositioned as a false positive, a true match, or a case requiring further investigation. A confirmed match may lead to blocking, rejecting, freezing, reporting, or escalation to legal counsel, depending on the applicable regime and facts.
Transaction monitoring is triggered by activity that breaches a rule, threshold, behavioral baseline, or analytical risk model. Its output is an alert or case requiring investigation. The outcome may be a documented closure, customer due diligence refresh, account restrictions, exit consideration, a suspicious activity report, or referral to another control function.
The operational error is to assume that a transaction monitoring alert should always stop a payment, or that a sanctions alert can wait for a routine case review. Payment interdiction decisions require clear, pre-defined escalation paths. Real-time payment environments make that discipline more urgent. A delayed sanctions decision can create a breach; an indiscriminate hold process can create customer harm and operational disruption.
Where the Controls Should Connect
Separate control objectives do not mean isolated operations. The best programs create controlled handoffs between sanctions, AML investigations, fraud, customer due diligence, and legal teams.
For example, a transaction monitoring investigation that identifies unusual activity involving a sanctioned jurisdiction should prompt review of payment parties, ownership information, trade documentation, and relevant sanctions exposure. Similarly, a sanctions screening false positive may still reveal weak customer data, a related entity not captured in onboarding, or activity requiring enhanced due diligence.
Shared intelligence is particularly valuable in complex cases involving shell companies, nested relationships, trade finance, correspondent banking, and virtual asset flows. Yet shared intelligence must be governed. Teams need consistent case identifiers, documented referral criteria, access controls, and decision records. Without this, the same risk can be investigated twice, or worse, fall between functional boundaries.
Building a Defensible Operating Model
An effective program begins with a clear allocation of accountability. Sanctions specialists should own the interpretation of sanctions obligations, list coverage, match-resolution standards, and urgent escalation protocols. AML teams should own monitoring scenario governance, alert investigation methodology, suspicious activity decisions, and model or rule validation. Both functions need common oversight where risks overlap.
Data governance is equally central. Screening quality depends on reliable names, identifiers, ownership data, and payment fields. Monitoring quality depends on complete transaction data, accurate customer risk ratings, expected activity profiles, and meaningful segmentation. If the source data is weak, adding more rules or lowering matching thresholds will not solve the underlying control problem.
Institutions should also preserve evidence that explains how decisions were made. That includes the lists and legal sources considered, alert details, analyst research, disposition rationale, approvals, and timing. Regulators and internal audit teams will assess more than whether an alert was closed. They will ask whether the institution applied the correct legal standard, used relevant information, escalated promptly, and could demonstrate consistent treatment across cases.
Regulatory change management deserves specific attention. New designations, shifting ownership guidance, enforcement actions, and jurisdiction-specific restrictions can alter screening obligations quickly. Practitioner-grade sanctions intelligence, including the ability to trace relevant source material across OFAC, OFSI, EU, and other authorities, helps teams assess what changed and whether screening rules, customer reviews, or payment controls need adjustment. Sherlocq is built for this type of source-backed, cross-border analysis.
The Question to Ask Before Buying or Tuning Technology
Technology decisions should start with the control objective, not a feature checklist. A payment screening engine must support timely interdiction, appropriate matching logic, list management, and investigator workflows. A transaction monitoring platform must support risk-based scenarios, segmentation, alert prioritization, investigation records, and ongoing validation. Some platforms offer both capabilities, but an integrated suite is not automatically better if either module cannot meet the institution’s risk, scale, or jurisdictional requirements.
Ask where decisions are made, who makes them, what information they need, and how quickly action must occur. Then test the system against actual cases: a common-name sanctions alert, a payment with incomplete originator data, a beneficial owner added after onboarding, and a cross-border transaction pattern that becomes suspicious only over several months.
The goal is not to produce fewer alerts at any cost. It is to produce decisions that are timely, explainable, and proportionate to risk. That is where sanctions screening and transaction monitoring stop being parallel compliance obligations and become a coherent financial crime control framework.